Connectors and secrets providers
A project can share external tools and external secret storage with every member, so nobody has to connect the same service twice.
Add connectors to a project
A project can have its own connectors – managed connections to MCP servers that give the agent access to external tools. A project connector is available to every cloud task and automation in the project, so you set it up once instead of each member configuring the same MCP server. Project admins add and remove connectors; members use them without any setup.
Add a connector to a project
Open the Projects page, select the project.
Under Connectors click Add Connector.
Choose the service, click Connect, and follow the provider's authorization flow. Sign in with the shared account you want the project to use.
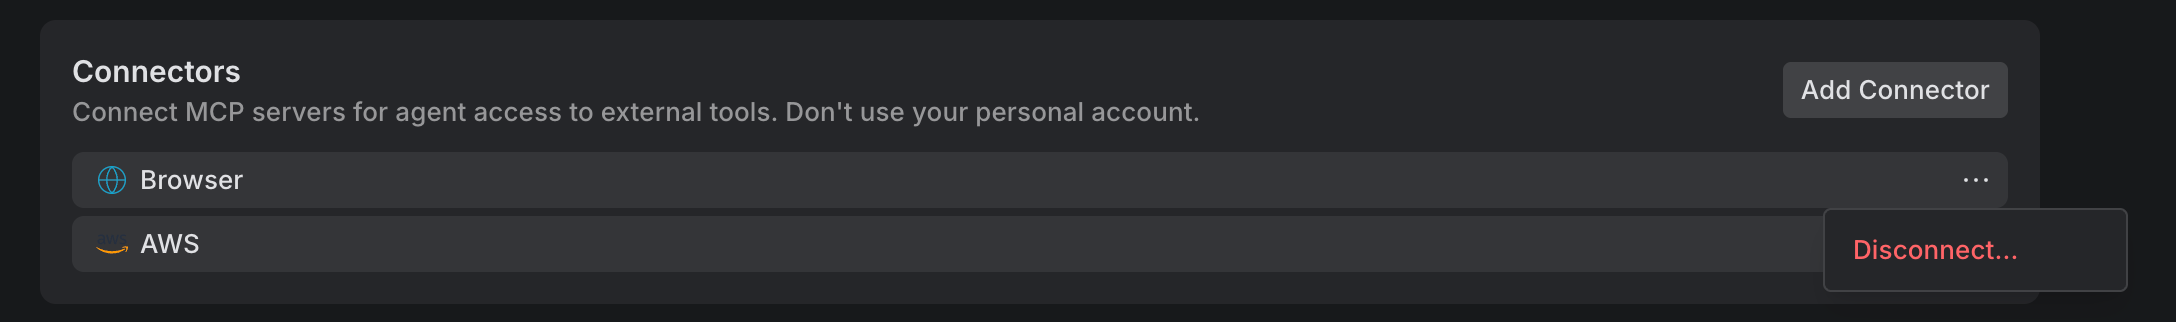
To remove a connector, click … next to it and select Disconnect. The project's tasks and automations then lose access to that MCP server's tools.
Add secrets providers to a project
A secrets provider is an external secrets manager that the project's environment configurations read secrets from, so a value your team already keeps in a vault doesn't have to be copied into JetBrains Air Teams. HashiCorp Vault is the first supported provider, and a project can connect several vaults – for example, one for production and one for staging.
JetBrains Air Teams stores the connection and its credentials, not the secrets. Each referenced secret is read from the vault when a cloud task or automation starts, and it's read from the cloud environment – so the vault has to be reachable from the internet. A vault that's only available inside your network doesn't work yet.
Project admins connect and disconnect providers. Members reference the secrets in the environment configurations they can edit.
Connect a secrets provider
Open the Projects page, select the project.
Under Secrets Providers, click Add Provider.
Under Connection, describe the vault:
Name – how the vault appears in environment configurations.
Type – the provider type. HashiCorp Vault is the only option for now.
Vault URL – the address of the vault, such as
https://vault.example.com:8200.Vault namespace – the namespace to read from, if you run Vault Enterprise. Leave it empty otherwise.
Under Authentication, provide the credentials JetBrains Air Teams authenticates with. Vault AppRole is the only method for now, so secrets are read on behalf of the AppRole rather than of the person running the task:
AppRole path – the path where the AppRole auth endpoint is mounted,
approleby default.Role ID and Secret ID – the credentials of the AppRole. Give it read access only to the secrets the project's tasks need.
Click Save.
Now the project's environment configurations can read variables from this vault. See Read a secret from HashiCorp Vault.